Unpacking DonutLoader — Malware Analysis (Case Lab 2/2)
Case Context
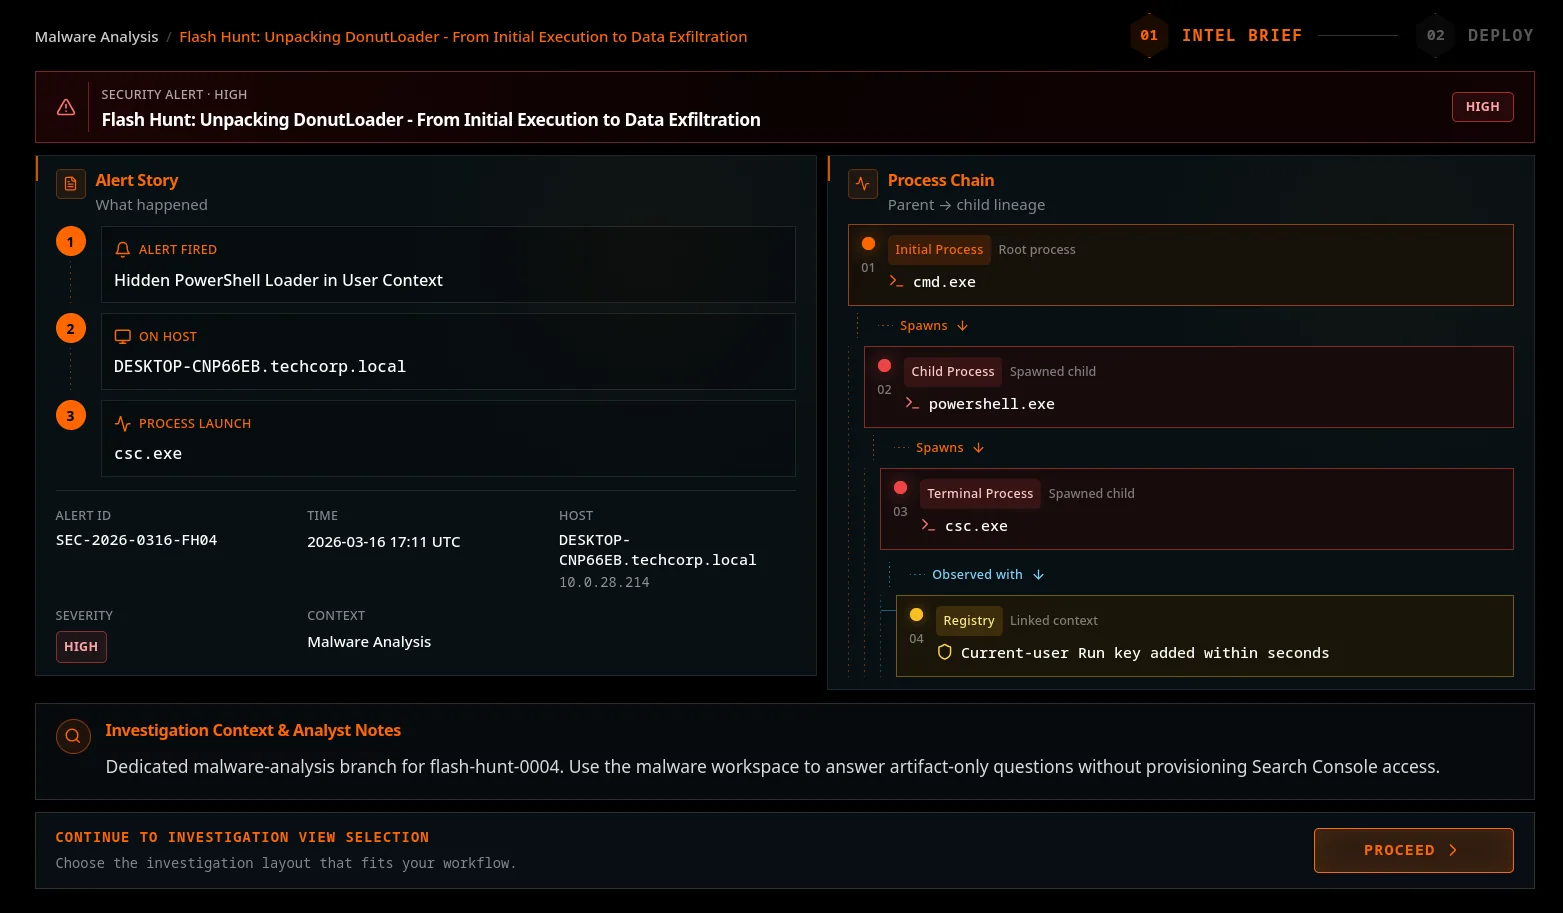
Part of a 2-lab Flash Hunt case on Threat Hunting Labs: Unpacking DonutLoader. This lab is the Malware Analysis angle (2 of 2), working four recovered artifacts directly in a REMnux workspace rather than pivoting through search-console telemetry.
Threat Hunting Labs has a strict no-public-writeup policy on active labs to protect scoring and leaderboards for other users, so this page is intentionally an overview: what I did and what I found, not the artifact internals or the specific answers that got me there.
Techniques Encountered
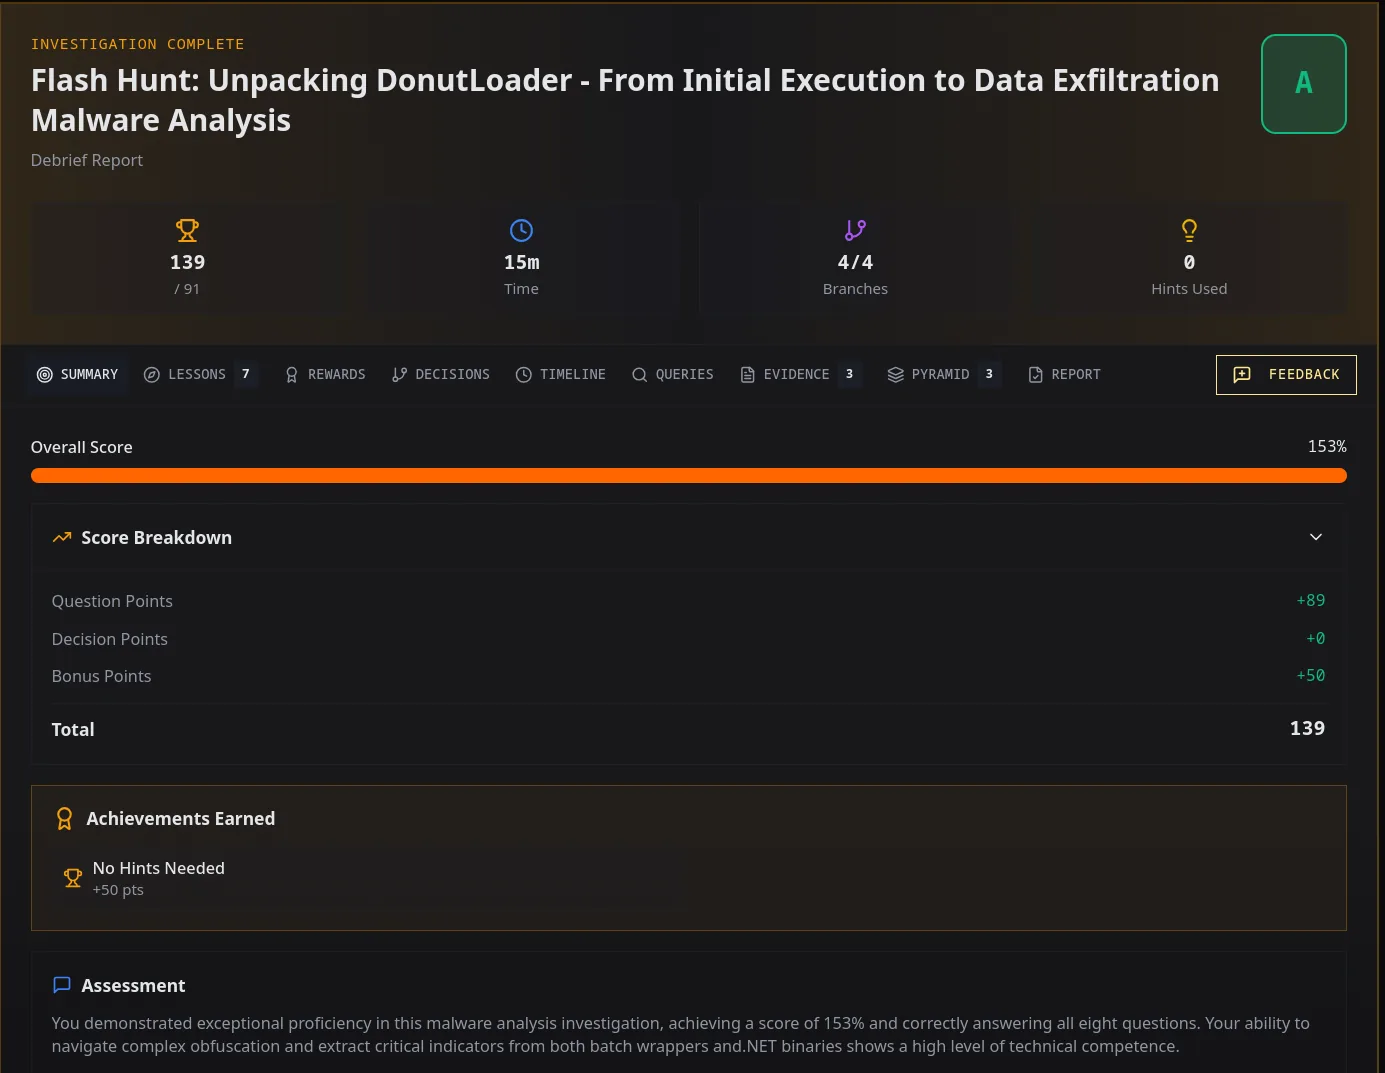
Four branch points across a scripting-layer loader, a compiled injector stage, and a pair of .NET credential stealers — execution and persistence through a self-staging loader and an autorun mechanism, defense evasion through layered obfuscation and an anti-sandbox gate, process injection into a legitimate host process, and credential access against browser and legacy credential stores. Cleared every branch with a perfect score and no hints used.
Prioritising Findings — Pyramid of Pain
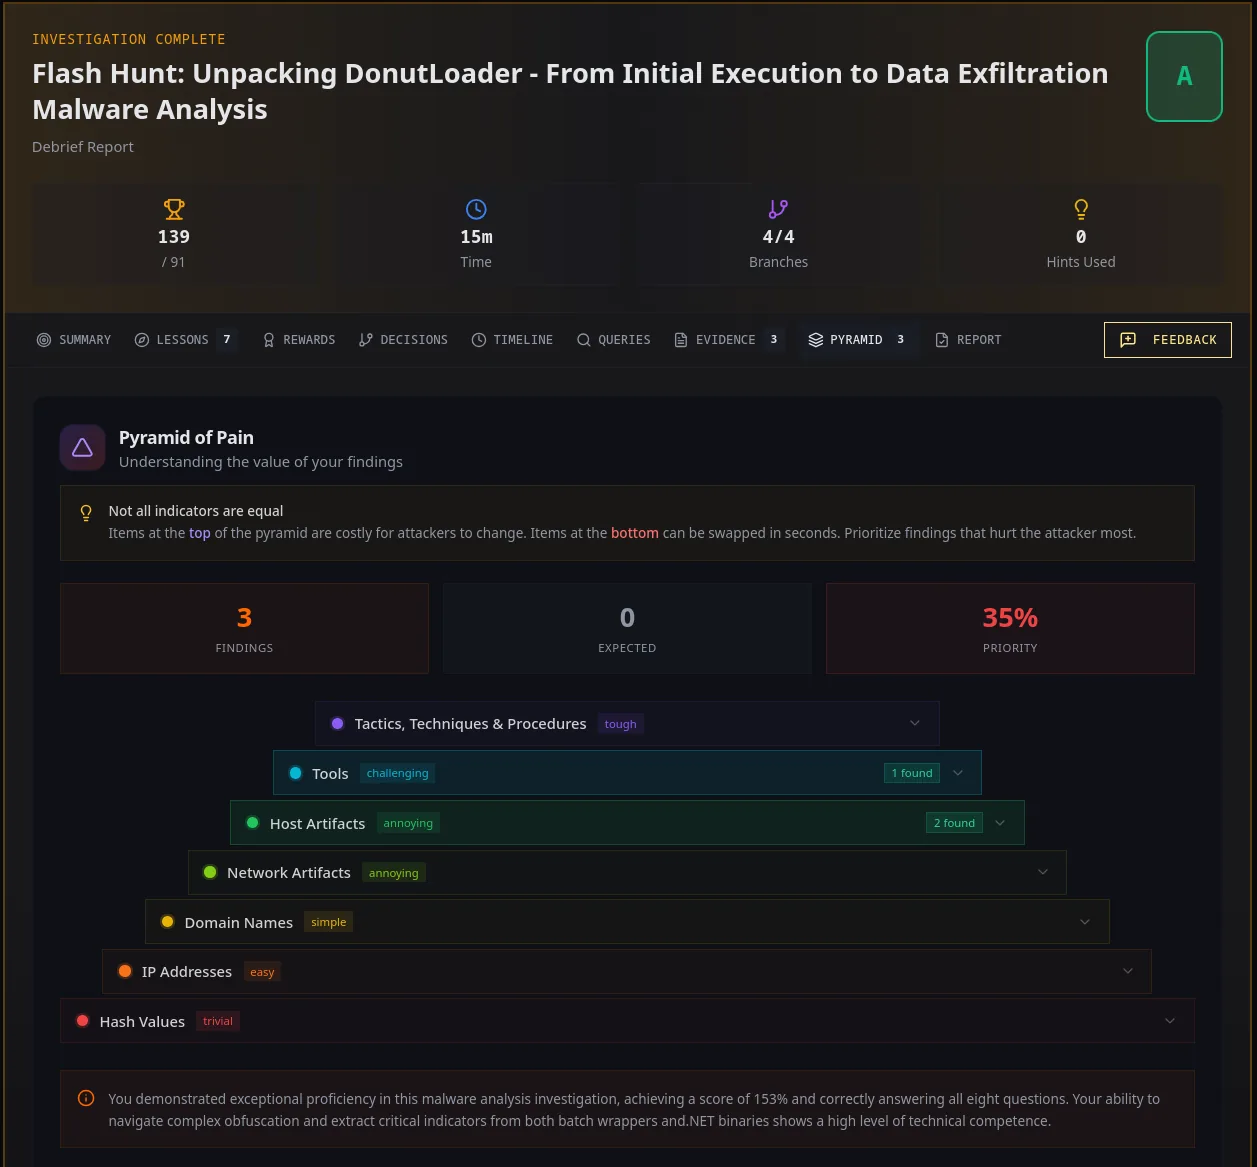
Findings sat mid-pyramid rather than at either extreme — tooling and host-artifact level rather than trivial network indicators, which tracks with a static-analysis exercise where the deliverables are the artifacts’ own internal mechanics rather than infrastructure that could be swapped out in seconds.
What I Practiced
- Statically recovering a payload a script stages for its own later execution, without letting the sample actually run its own unpacking chain
- Reading obfuscated scripting-layer tradecraft and separating the handful of load-bearing lines from a much larger body of deliberate noise
- Recognising string-concatenation obfuscation of API, library and process identifiers inside inline compiled code, and reassembling them by hand
- Distinguishing a lookup used purely as an execution guard from the lookup that actually feeds a later, more consequential operation, where both use the same obfuscation trick
- Tracing a full process-injection sequence through renamed wrapper calls back to the underlying API chain, including a persistence/re-injection loop
- Locating key-derivation material and ciphertext boundaries inside a single decoded blob for a symmetric-encryption payload
- Static string-table extraction against .NET assemblies to enumerate what credential stores a sample targets
Credential
Earned a Distinction (100% score) on this Flash Hunt lab.
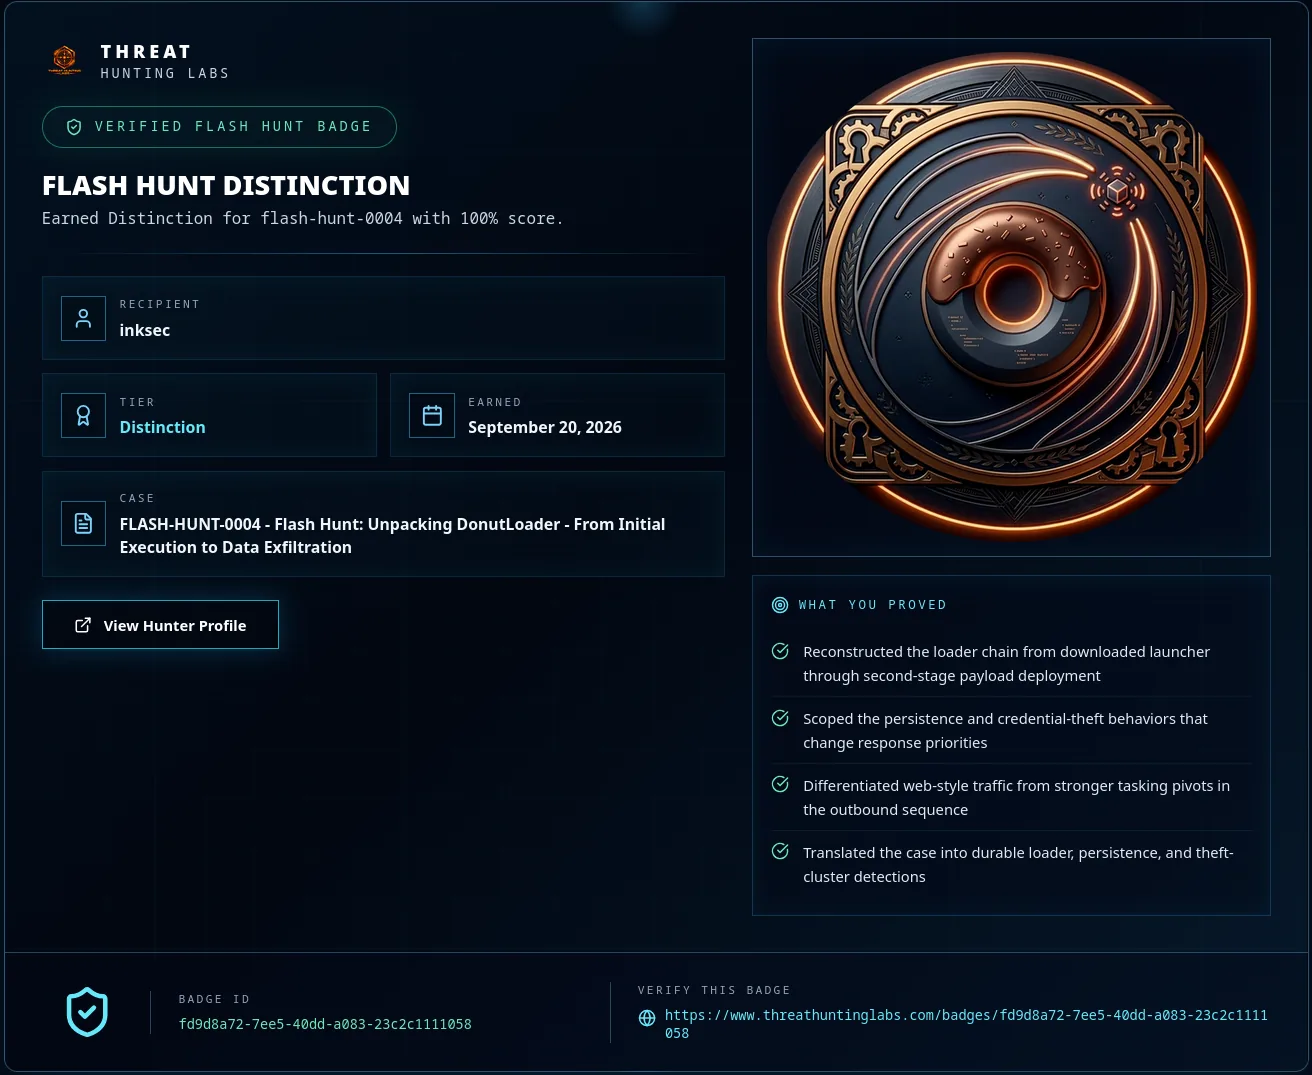
Verify: https://www.threathuntinglabs.com/badges/fd9d8a72-7ee5-40dd-a083-23c2c1111058
This is the Malware Analysis half of the DonutLoader case. The Investigation angle ([[unpacking-donutloader-threat-hunt]]) works the same intrusion from host and network telemetry.