M365 Mailbox Intrusion — Threat Hunt (Case Lab 1/3)
Case Context
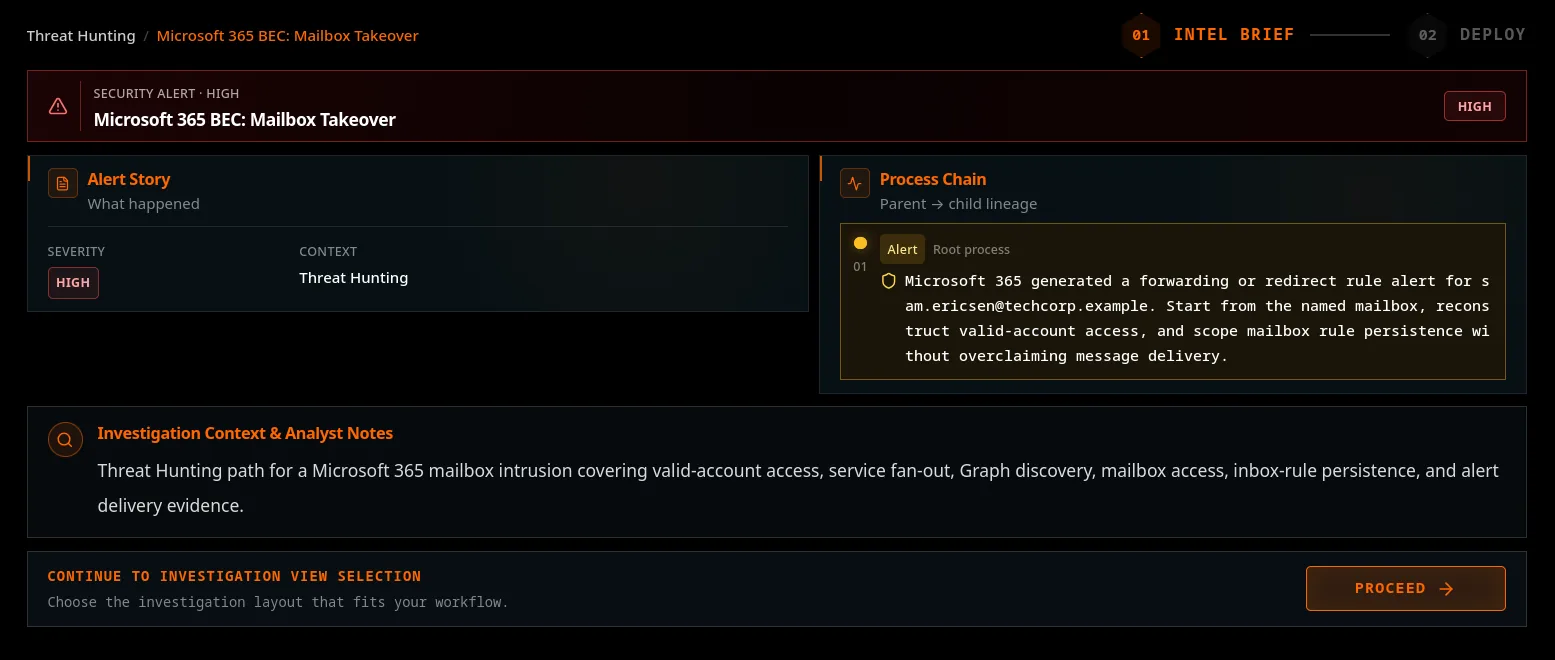
Part of a 3-lab investigation case on Threat Hunting Labs. This lab is the Threat Hunt angle (1 of 3), scoped to reconstructing valid-account access, Microsoft 365 service fan-out, Graph discovery, mailbox collection and inbox-rule persistence from a BEC alert against a named mailbox.
Threat Hunting Labs has a strict no-public-writeup policy on active labs to protect scoring and leaderboards for other users, so this page is intentionally an overview: what I did and what I found, not the queries or the specific answers that got me there.
Techniques Encountered
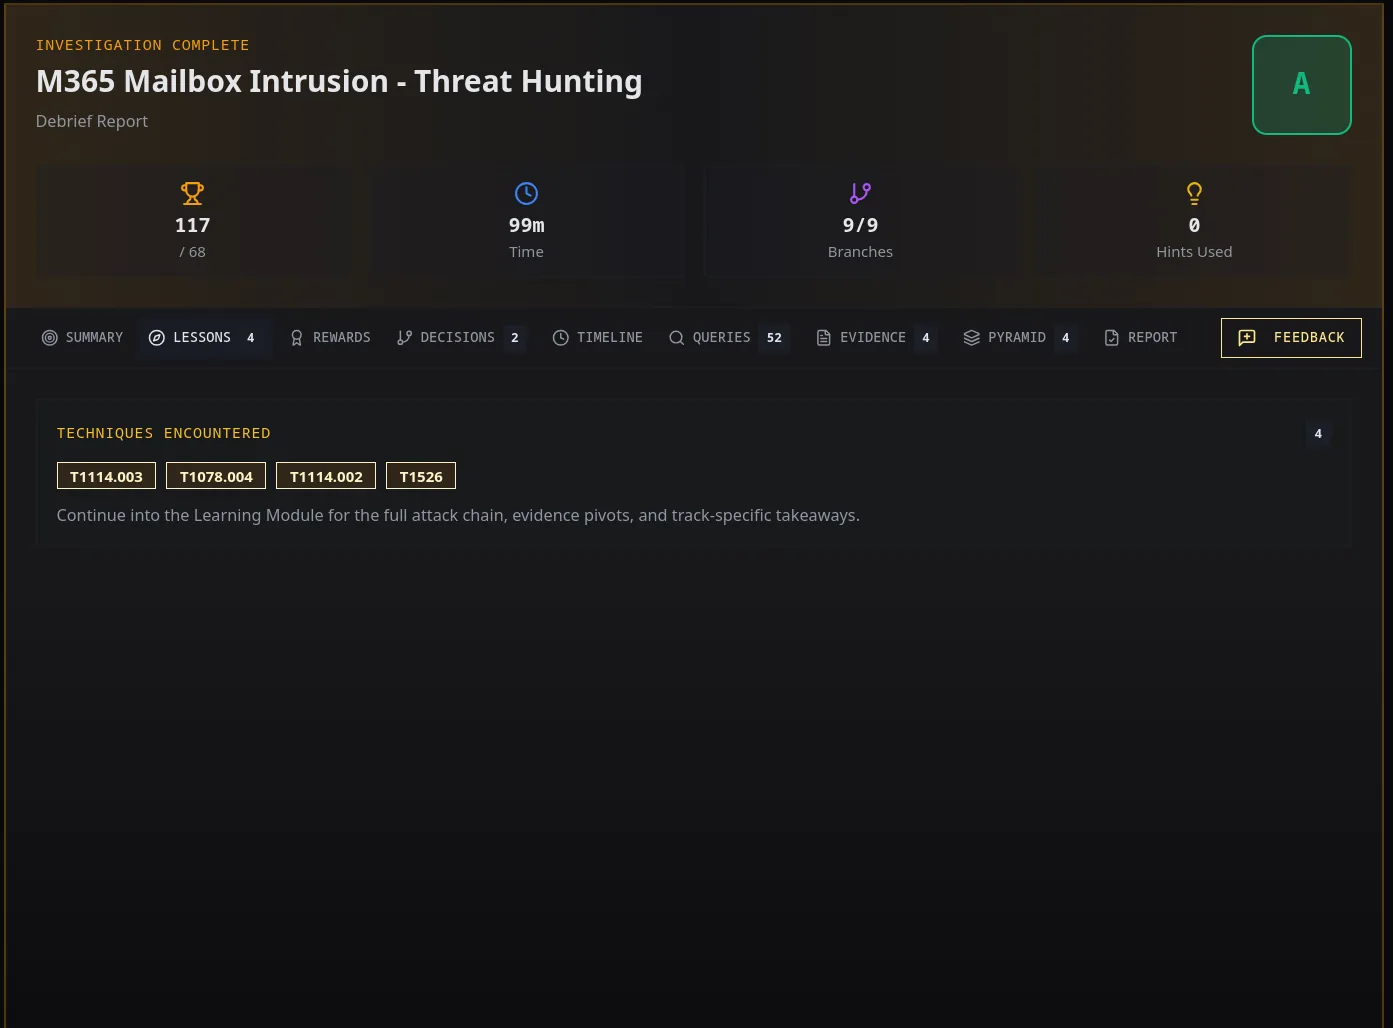
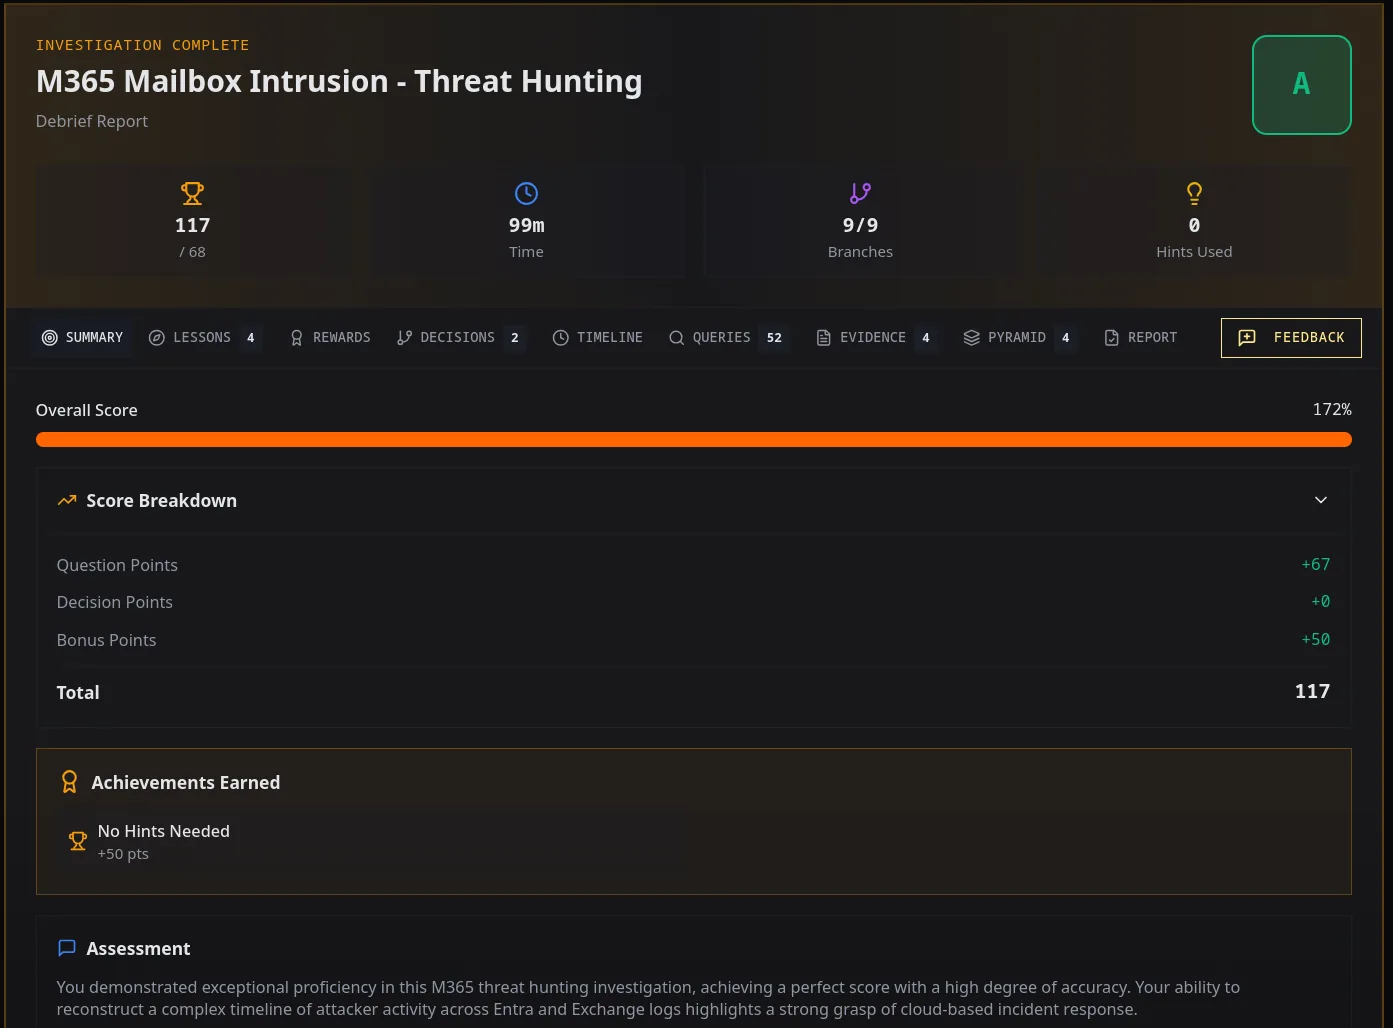
Nine branch points across Entra interactive and non-interactive sign-in logs, Microsoft Graph activity, Exchange mailbox audit and Exchange message trace, tying a compromised session to Graph enumeration, OWA mailbox reads and inbox-rule persistence. Cleared every branch with a perfect score and no hints used.
Prioritising Findings — Pyramid of Pain
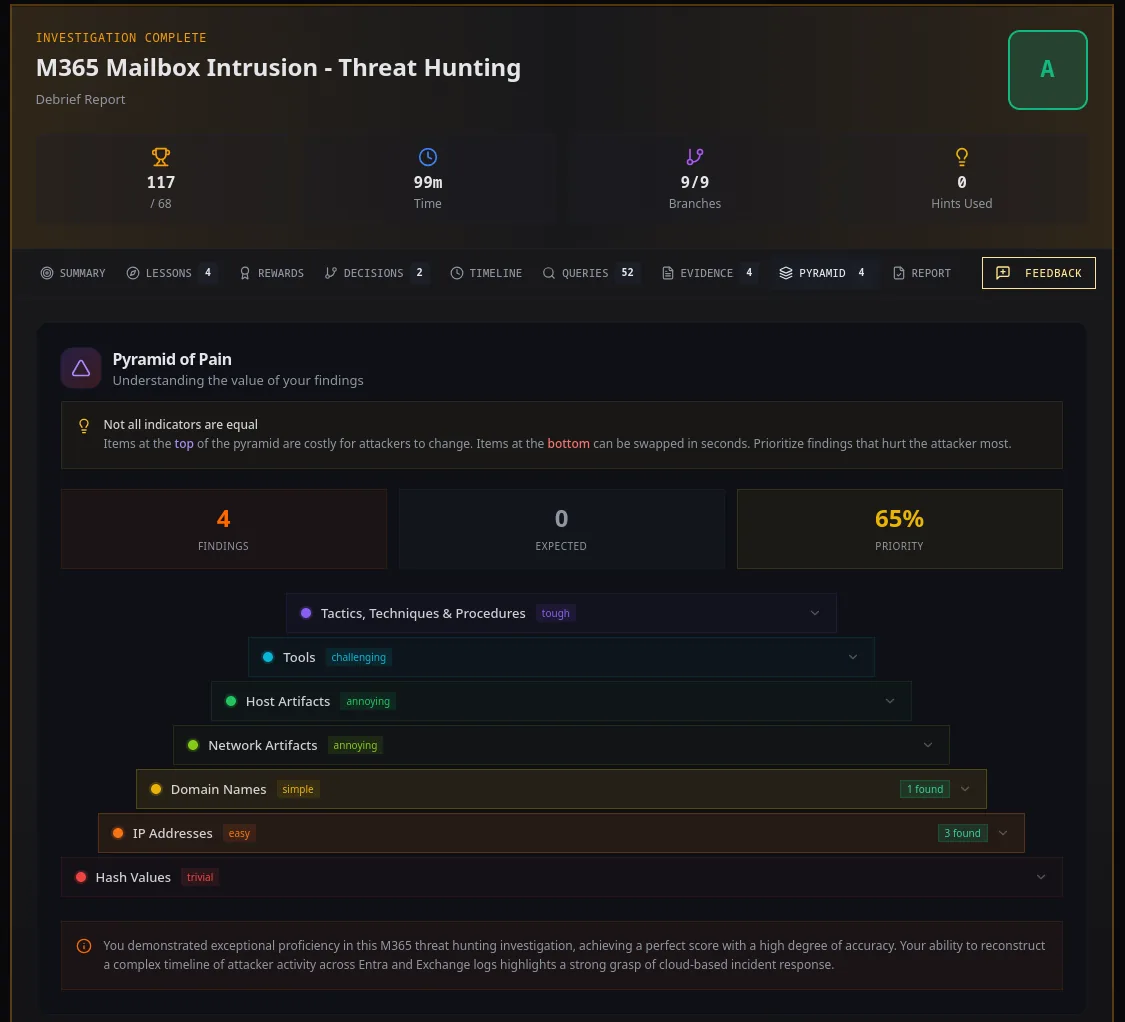
Findings sat at the bottom of the pyramid — IP addresses and a domain, the tier an attacker can swap out in seconds — rather than anything at the TTP or tooling level. That tracks with an intrusion that never touched malware or custom tooling and instead rode legitimate Microsoft 365 session and API activity the entire way through.
What I Practiced
- Reasoning about completion rather than mere presence when scoping “the first login” — a sign-in record existing doesn’t mean the flow finished, and the audit fields available here repeatedly rewarded checking the actual outcome over the first chronological hit.
- Treating a stolen session token as portable infrastructure rather than a single event — following the token across sign-in tables surfaces replay in a way that address-hopping alone doesn’t.
- Reading Microsoft Graph activity by HTTP method and status code before reading it by endpoint name, since that’s what actually separates a read from a write and a success from a refusal.
- Working inside a flattened custom-log schema where the fields a hunt needs exist only inside nested, escaped JSON rather than as queryable columns — validating schema against known-good events before trusting a negative result.
- Keeping detection and delivery as separate facts. An alert firing correctly in telemetry is not the same fact as a human ever seeing it, and the case only resolves cleanly once those two are kept apart.
Credential
Earned the completion certificate for this 3-lab case (Threat Hunt, Incident Response, Detection Engineering).
Verify: https://www.threathuntinglabs.com/certificates/i24dJJsDrmmU