
mdr analyst
// Melbourne, Australia
$whoami
Tate Pannam// inksec
$cat ~/role.txt
SOC Analyst| Blue Team | Melbourne, AU
$cat ~/stats.txt
$cat ~/focus.txt
CCDL1 · SC-200 · 13Cubed ×3 done · daily SIEM sims · open to SOC & CSIRT roles
view blue team portfolio → // recent activity
last update 5 days ago
rss ↗last 30 days8 labs3 alerts0 posts6 rank snapshots
// portfolio
Not courses — real work. Every investigation, writeup, and lab below is publicly documented and verifiable.
Primary focus
Blue Team Operations
123
Investigations
101
ATT&CK techniques
123+
YouTube walkthroughs
- Investigated 123+ live security alerts — each triaged, escalated, and written up with full methodology
- Completed 216+ lab scenarios across cloud forensics, malware analysis, and incident response
- Published every finding publicly — demonstrating ability to explain complex security events in plain writing
- Certified: CDSA · BTL1 · CCDL1 · 13Cubed · SC-200
offensive background
0x74617465.sh
top 1%
HTB
55+
boxes
11
pro labs
CPTS
certified
explore →
// certifications
HTB Academy · November 2025
CDSA
Certified Defensive
Security Analyst
Security Analyst
verify on credly ↗
Security Blue Team · April 2026
BTL1
Blue Team Level 1
Certified
Certified
verify on credly ↗

CyberDefenders · July 2026
CCDL1
CyberDefenders Level 1
Certified
Certified
verify on credly ↗

13Cubed · August 2026
13Cubed
Investigating Windows
Endpoints · Gold
Endpoints · Gold
verify on credsverse ↗

13Cubed · August 2026
13Cubed
Investigating Windows
Memory · Gold
Memory · Gold
verify on credsverse ↗

13Cubed · September 2026
13Cubed
Investigating macOS
Endpoints · Gold
Endpoints · Gold
verify on credsverse ↗

Microsoft · August 2026
SC-200
Security Operations
Analyst Associate
Analyst Associate
verify on microsoft ↗
CPTS
Certified Penetration Testing Specialist
BSCP
Burp Suite Certified Practitioner
CWES
Certified Web Exploitation Specialist
eJPT
Junior Penetration Tester
ICCA
INE Certified Cloud Associate
SAL1
Security Analyst Level 1
Cert IV
Cyber Security · Victoria University
CDCA
Cyber Defense Certified Analyst
CDETH
Certified Detection Engineer & Threat Hunter
ATH
Architecting the Hunt (13Cubed)
CCSA
Cybrixen Certified SOC Analyst
S1 Admin
SentinelOne Security Administrator
S1 IR
SentinelOne Incident Responder
// Day X: becoming a SOC analyst
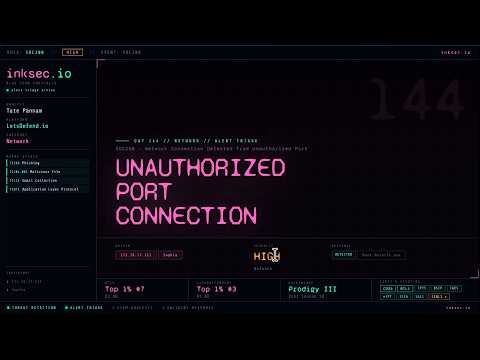
Every day: one real SIEM alert, triage out loud, documented. Covering log correlation, IOC analysis, containment decisions, and escalation methodology — real analyst thinking, not just answers.
Latest Episode · 2026-10-14
SOC208 — Network Connection Detected from Unauthorized Port
A phishing email delivered a zip disguised with .bin that held a .NET infostealer. It read Outlook profile data from the registry and sent it out over SMTP 587 to a Turkish mail server. Contained, credentials reset, IOCs blocked. I lost marks for skipping the OS logs, and the lesson was to check host artifacts before relying on the sandbox.
 ▶
// tools & stack
SIEM · Log Analysis
Network Forensics
Endpoint · Memory Forensics
Threat Intel · OSINT
// get in touch
Currently working
in MDR
in MDR
Always happy to talk DFIR, threat hunting or lab writeups.
Melbourne-based. Reach out on any of these.